24/7 Managed SOC Services: Critical Security for Indian Businesses
Why 24/7 Managed SOC Services Are Becoming Critical for IT Teams in India
For IT businesses, cybersecurity does not follow office hours. Applications, networks, cloud environments, endpoints, and business systems can remain active around the clock, creating opportunities for suspicious activity at any time. 24/7 managed soc services give organizations access to continuous security monitoring and security operations support beyond the limits of a traditional working-day model.
This approach is becoming relevant for Indian IT businesses that need to maintain visibility across complex environments while allowing their internal teams to focus on infrastructure, applications, operations, and business priorities.
What 24/7 Managed SOC Services Mean for IT Businesses
24/7 managed SOC services provide continuous security monitoring, analysis of security events, threat detection, and support for investigating and escalating potential incidents.
A Security Operations Center, or SOC, brings together people, processes, and security technologies to monitor an organization's environment. In a managed model, an external security team performs agreed monitoring and operational activities on behalf of the organization.
The objective is not simply to collect large volumes of security alerts. It is to identify events that may indicate a security problem, analyze them in context, and help the organization respond through a defined process.
For IT companies operating systems outside conventional business hours, this continuous model can help reduce periods where security events may otherwise receive limited attention.
Why Managed SIEM Providers Matter to Continuous Security Monitoring
A SOC depends heavily on the quality and availability of security information. Security Information and Event Management, or SIEM, technology can bring together logs and security events from relevant systems and help identify relationships between different activities.
This makes the selection of managed siem providers an important consideration for businesses looking at managed security operations. A provider should be evaluated not only on its ability to collect security data but also on how that information supports monitoring, analysis, investigation, and escalation.
For an IT organization, SIEM and SOC capabilities work together. SIEM can provide the security-event visibility, while SOC personnel can analyze that information and determine which events require further attention.
This combination can create a more organized approach to security monitoring than relying on disconnected tools and manual reviews.
Why Traditional Monitoring Can Become Difficult for IT Teams
Many IT businesses already have security technologies in place. Firewalls, endpoint protection, identity controls, vulnerability-management activities, and other defensive measures may all contribute to an organization's security posture.
However, technology alone does not guarantee continuous monitoring.
Internal IT teams often have broad responsibilities. The same personnel may manage infrastructure, troubleshoot applications, support users, maintain cloud environments, and handle security-related tasks. Continuously reviewing security alerts alongside these responsibilities can become operationally challenging.
There is also the issue of alert volume. Security systems can generate numerous notifications, and not every alert represents a genuine incident. Without an organized process for reviewing and prioritizing events, important signals can become difficult to distinguish from routine activity.
A managed SOC can supplement internal resources by providing dedicated security monitoring and analysis as part of an established operating model.
How a Managed SOC Fits Into an IT Environment
A managed SOC typically starts by establishing visibility into the security-relevant systems within an organization's environment. Depending on the organization's requirements, this may involve security events from network infrastructure, endpoints, applications, cloud environments, identity systems, and other relevant sources.
The collected information is then monitored and analyzed for suspicious patterns or events.
When an alert requires investigation, security analysts can review the available information to understand what occurred and whether further action may be necessary. Events can then be prioritized and escalated according to the agreed procedures.
This creates a continuous operational cycle:
Security data → monitoring → alert analysis → investigation → escalation → response
The precise responsibilities vary according to the service arrangement and the organization's environment. However, the underlying purpose remains consistent: turn security-event data into useful security operations.
The Operational Value of Continuous Monitoring
The biggest advantage of continuous monitoring is visibility beyond normal working hours.
Suppose an IT company experiences an unusual authentication event late at night. If monitoring depends entirely on an internal team working standard hours, the event may not receive immediate human attention. A continuous managed SOC model provides a mechanism for such events to be monitored and assessed outside the organization's regular schedule.
There is also a resource benefit.
Instead of requiring internal employees to spend significant time continuously watching security alerts, an organization can use managed security operations to supplement its existing team. Internal personnel can remain involved in higher-level decisions, investigations, remediation, and business-specific activities where their knowledge is most valuable.
The model can therefore help create a clearer division of responsibilities between day-to-day IT operations and continuous security monitoring.
A Practical Example for an Indian IT Company
Imagine an Indian IT services organization supporting applications and infrastructure for business customers in multiple time zones.
Its systems operate continuously, even when the company's primary office is closed. One night, several unusual authentication events appear across its environment. Individually, these events may not immediately indicate a serious problem. When examined together, however, they may require further investigation.
A managed SOC can monitor these events, correlate available information, investigate the activity, and escalate the matter according to the agreed process.
The internal IT team can then use the available information to determine the appropriate business and technical response.
The important point is that continuous monitoring does not mean every alert becomes an emergency. It creates a structured mechanism for identifying which events deserve attention.
What IT Businesses Should Check Before Selecting a Managed SOC
Choosing a managed SOC requires more than looking for a provider that offers round-the-clock monitoring. IT businesses should consider how the service fits their existing environment and security processes.
- Coverage of the organization's relevant systems and security data
- Continuous monitoring and alert-review capabilities
- Approach to investigating suspicious security events
- Defined escalation and communication procedures
- SIEM integration and security-event visibility
- Reporting and documentation requirements
- Compatibility with existing IT and security processes
- Ability to adapt as the organization's environment changes
- Clear responsibilities between the provider and internal teams
These considerations help organizations understand what they are actually receiving rather than evaluating a managed SOC solely on the promise of continuous availability.
Managed SOC and Internal IT Teams Can Work Together
A common misconception is that adopting managed SOC services means removing the need for an internal IT or security team.
In practice, the two can have complementary roles.
Internal teams understand the organization's applications, infrastructure, business priorities, users, and operational dependencies. A managed SOC can contribute continuous monitoring, security analysis, and operational support.
This division can be especially useful for organizations that need broader security coverage but do not want their internal IT personnel to carry the entire burden of round-the-clock alert monitoring.
The result is not necessarily a replacement for internal expertise. Instead, it can extend the organization's security operations capabilities.
Security Governance and the Indian IT Sector
Security monitoring should also form part of a broader governance approach.
Indian IT organizations may have contractual security obligations, customer requirements, internal policies, and applicable regulatory or data-protection responsibilities. The exact requirements differ according to the organization's activities and the nature of the information it handles.
A managed SOC can support operational security processes, but it should not be treated as a substitute for broader governance, risk management, security policies, access controls, vulnerability management, or incident-response planning.
Organizations should evaluate how continuous monitoring fits into their overall security framework and applicable obligations.
Making Continuous Security Monitoring More Practical
For IT businesses, the question is increasingly less about whether security events can occur outside office hours and more about how those events will be monitored and handled.
A structured managed SOC approach can provide continuous visibility while allowing internal teams to concentrate on their core technical responsibilities. When combined with appropriate SIEM capabilities, defined escalation procedures, and clear ownership, it can create a more consistent security-monitoring operation.
For Indian IT businesses operating increasingly connected and continuously available environments, 24/7 managed soc services can serve as an operational layer between security technology and the people responsible for protecting the business.
The goal is not simply to monitor more alerts. It is to create a dependable process for identifying meaningful security activity, investigating potential threats, and ensuring that important events reach the right people when they need to know.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - sales@ibntech.com
Categories
- Artificial Intelligence (AI)
- Technology
- Business
- Education
- Science
- Lifestyle
- Healthcare
- Entertainment
- Politics
- Environment
- Travel
- Finance
- Automobile
- News
- Art
- Causes
- Crafts
- career
- Dance
- Drinks
- Film
- Fitness
- Food
- Games
- Gardening
- Health
- Home
- Literature
- Music
- Networking
- Other
- Party
- Religion
- Shopping
- Sports
- Theater
- Wellness
Read More
The Healthcare Electronic Data Interchange Market is expanding as healthcare organizations accelerate administrative automation and digital transaction processing. The market was valued at USD 4.52 billion in 2024 and is projected to reach USD 13.97 billion by 2035, growing at a CAGR of 10.8% during 2026–2035. Healthcare providers and payers are increasingly using EDI to exchange claims,...
A detailed engineering evaluation demonstrates that the Differential Sensor Market Analysis is fundamentally defined by an instrument's ability to maintain micro-level accuracy while isolating and surviving severe static line pressures. When measuring flow or tank levels in petrochemical processes, the differential pressure of interest might measure merely 10 to 50 millibars, while the baseline...
The GCC Digital Healthcare Market was valued at approximately USD 5.5 billion in 2024 and is projected to grow from USD 6.28 billion in 2025 to USD 23.83 billion by 2035, registering a CAGR of 14.26% during 2025–2035. Increasing adoption of telemedicine, artificial intelligence, remote patient monitoring, cloud technologies, and government-led digital transformation initiatives are...
India Edible Oils Fats Market is becoming an important part of India's food and agricultural economy as households, restaurants, and food manufacturers continue to use edible oils and fats in everyday food preparation. These ingredients support a variety of cooking methods and contribute to the taste, texture, and performance of different food products. Changes in lifestyle, growing interest in...

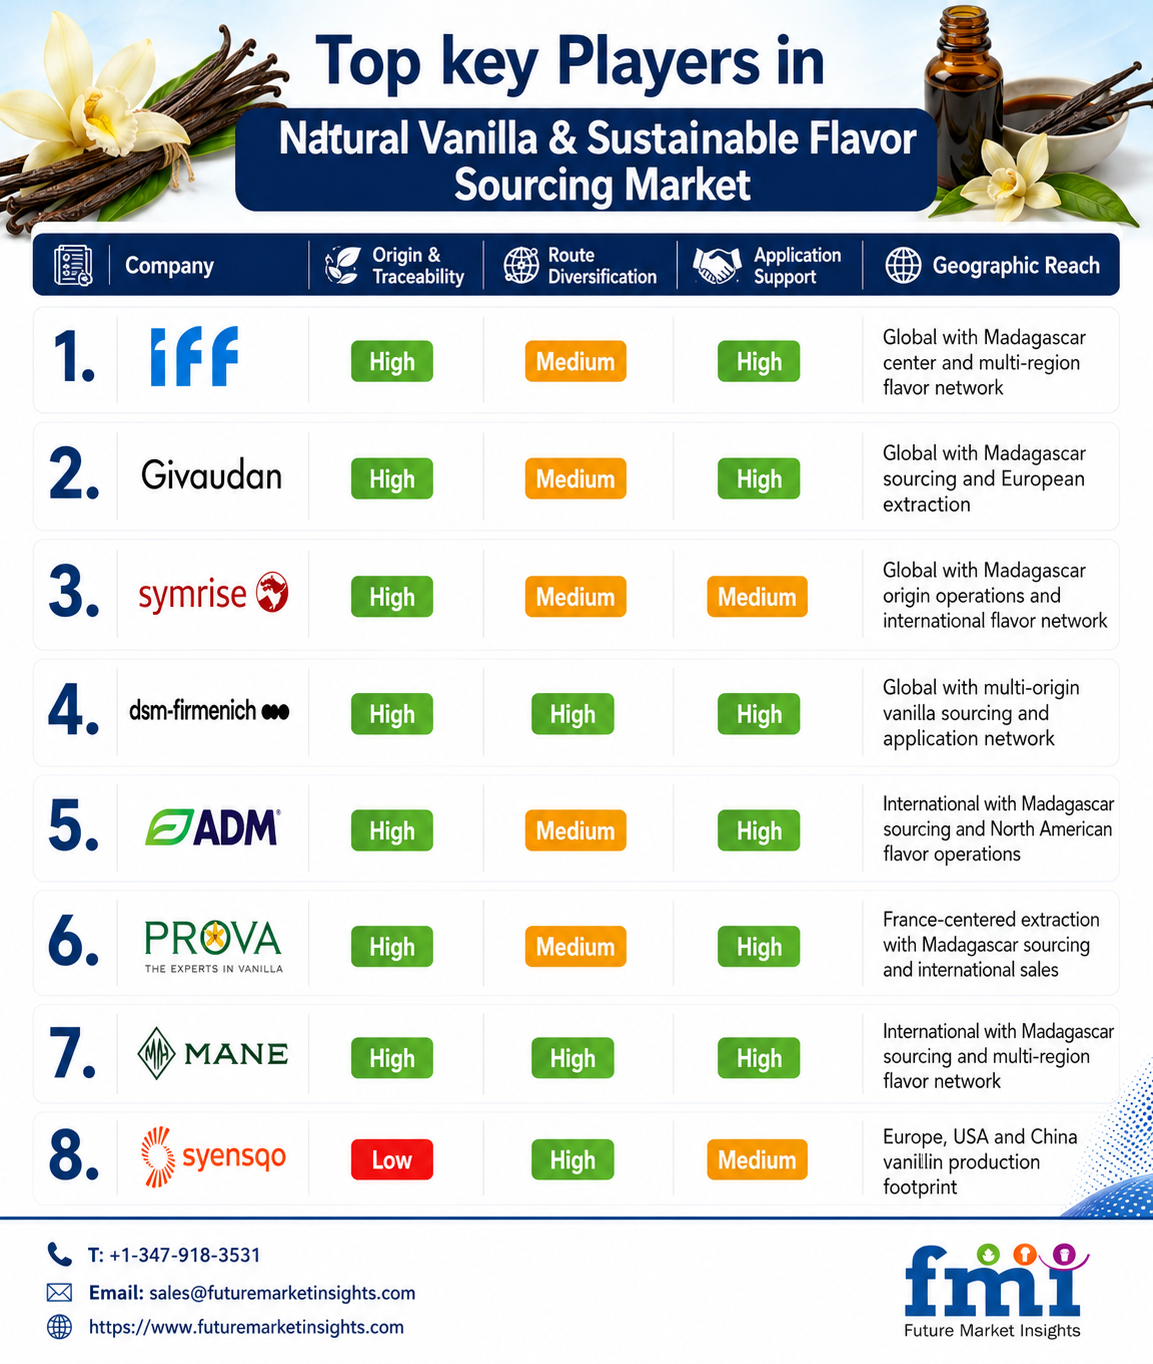
NEWARK, Del., August 24, 2026 — The global Natural Vanilla & Sustainable Flavor Sourcing Market is entering a period of strong expansion as food manufacturers place greater emphasis on ingredient traceability, sustainable sourcing, origin documentation, and reliable flavor performance. According to the latest market assessment, the market is valued at USD 1.7 billion in 2026 and is...