Managed SOC Services in India: Critical Security Visibility for IT Businesses
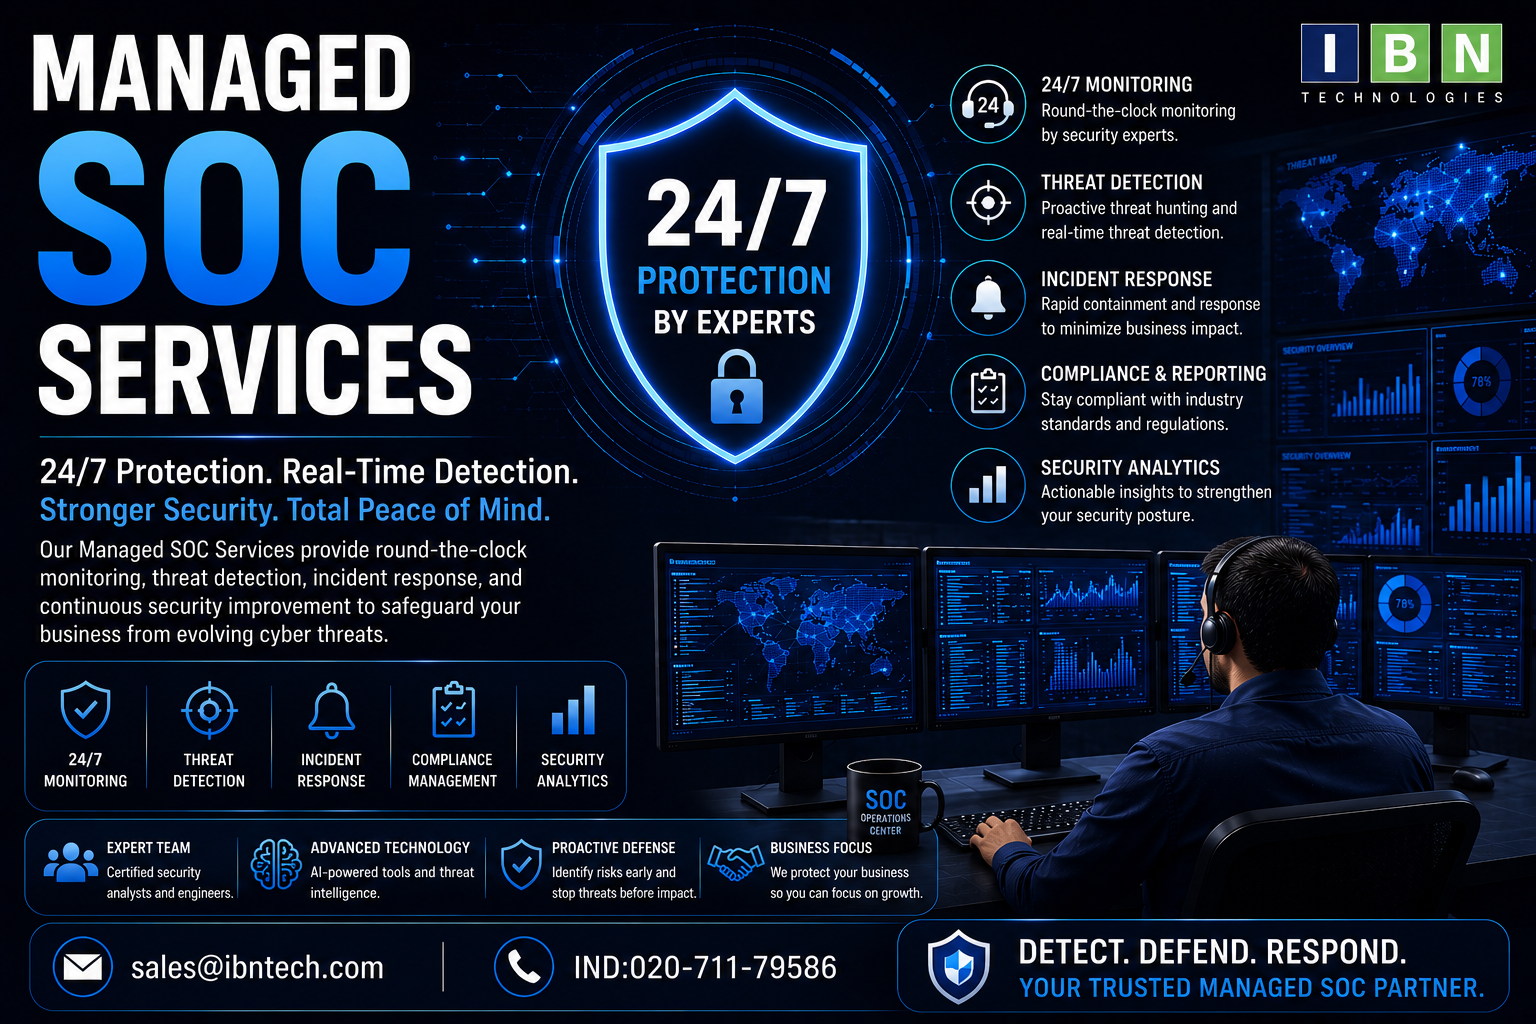
How Managed SOC Services Give Indian IT Teams a Stronger Security Operation
As Indian IT businesses expand cloud environments, applications, remote access, and connected infrastructure, security teams must monitor a growing volume of activity. Security events can originate from endpoints, networks, identities, applications, and other parts of the technology environment.
managed soc services provide an organized way to monitor security activity, investigate potential threats, and escalate incidents through a defined security operations process. Instead of requiring an organization to build every SOC function internally, a managed model can provide external operational support alongside existing IT and security teams.
What are managed SOC services for Indian IT businesses?
Managed SOC services are externally delivered security operations capabilities that help organizations monitor security events, identify potential threats, investigate suspicious activity, and support incident escalation. For Indian IT businesses, a managed SOC can extend security monitoring capabilities while allowing internal teams to retain responsibility for business decisions and remediation.
A managed SOC typically works alongside an organization's existing cybersecurity technologies and processes. The service model and monitoring scope depend on the organization's environment and agreed operational requirements.
Why does managed SOC monitoring matter for IT businesses?
IT environments generate security information continuously. Authentication events, endpoint activity, network behavior, application events, and other signals can provide valuable indicators of suspicious activity.
The challenge is turning those signals into useful security decisions.
A managed SOC introduces a structured process for reviewing security events and determining which activity requires investigation. This can help internal IT teams focus their attention on meaningful security issues rather than manually examining every available alert.
As Indian enterprises scale digital operations, maintaining security visibility becomes an ongoing operational requirement rather than a one-time technology project.
How do top SOC providers support IT security operations?
Organizations researching top soc providers should look beyond feature lists and examine how a provider actually operates.
A capable managed SOC should have a clearly defined approach to monitoring, alert analysis, investigation, escalation, and reporting. The organization should also understand which systems can be monitored and what responsibilities remain with the internal team.
For example, a provider may identify and investigate suspicious activity, while the organization's internal IT team remains responsible for approving a particular remediation action. Clear ownership helps prevent delays when an incident requires a coordinated response.
Why can building a SOC internally be challenging?
An internal SOC requires more than security software. Organizations need people, processes, monitoring infrastructure, security data, incident procedures, and ongoing operational management.
IT teams may already be responsible for infrastructure, applications, user support, cloud environments, and other technology operations. Adding continuous security monitoring to these responsibilities can create competing demands.
A managed model can provide external operational capacity for defined SOC functions. This does not eliminate the need for internal security ownership. Instead, it can create a division of responsibilities between the managed SOC and the organization's existing team.
What should an IT business evaluate before choosing managed SOC services?
The evaluation should begin with the organization's technology environment.
IT leaders should identify critical systems, applications, endpoints, network environments, and other assets that require security visibility. They should then determine which security events need monitoring and how potential incidents should be escalated.
Which factors matter when evaluating a managed SOC?
- Monitoring coverage across critical environments
- Security event collection and analysis
- Alert triage and investigation
- Threat detection processes
- Incident escalation procedures
- Reporting and operational visibility
- Integration with existing security technologies
- Defined responsibilities between provider and internal teams
- Processes for reviewing and improving monitoring coverage
These factors provide a more practical basis for evaluating a managed SOC than simply comparing the number of services advertised by different providers.
How does a managed SOC improve security operations?
A managed SOC can bring consistency to security monitoring and investigation.
Instead of leaving security alerts across multiple systems for internal teams to review independently, a managed SOC can provide a defined operational process for examining relevant events.
It can also help establish clear escalation paths. When suspicious activity is identified, the organization should know who receives the information, what details are provided, and which team is responsible for the next action.
This structure can make security operations easier to manage, particularly when internal teams have limited time for continuous monitoring.
What does a practical managed SOC workflow look like?
A typical workflow begins with collecting relevant security events from agreed technology environments.
Those events can then be monitored and analyzed for suspicious activity. Potentially important alerts are investigated to determine whether they represent a genuine security concern.
When an incident requires further action, the finding can be escalated according to predefined procedures. Internal teams can then take the appropriate organizational or technical action based on their responsibilities.
The exact workflow varies by service model, but the underlying objective remains the same: create a repeatable process for turning security activity into actionable information.
Can managed SOC services support compliance requirements?
Security monitoring can contribute to broader information-security and governance programs.
Depending on the organization's obligations, areas such as access management, logging, incident management, data protection, and security controls may be relevant. Frameworks such as ISO/IEC 27001 can also form part of an organization's information-security management approach.
A managed SOC can provide useful monitoring and operational information, but it does not independently establish compliance. Compliance depends on the organization's overall policies, controls, governance, implementation, and evidence.
IT businesses should therefore treat managed SOC operations as one component of a wider cybersecurity and governance strategy.
What should IT leaders ask a managed SOC provider?
A simple conversation can reveal whether a service is suitable for the organization's environment.
Ask which systems can be monitored, how alerts are investigated, how incidents are escalated, what reporting is available, and where responsibility moves from the provider to the internal team.
It is also important to understand how the service will adapt as the organization's technology environment changes.
The right question is not simply, "Does this provider offer managed SOC services?" A more useful question is, "Does its operating model match the security requirements of our IT environment?"
Frequently Asked Questions
What are managed SOC services?
Managed SOC services provide external security operations support for monitoring, threat detection, investigation, and incident escalation across defined technology environments.
Are managed SOC services suitable for IT businesses?
They can be suitable for IT businesses that need structured security monitoring but prefer to supplement internal capabilities with an external security operations function.
What should businesses consider when choosing a managed SOC?
Businesses should evaluate monitoring coverage, detection and investigation processes, escalation procedures, reporting, technology integration, and clearly defined responsibilities.
For Indian IT businesses, security monitoring needs to keep pace with increasingly complex technology environments. managed soc services can provide a structured operational layer for detecting suspicious activity, investigating potential threats, and escalating incidents while complementing internal IT teams. The most useful approach is one aligned with the organization's systems, security priorities, responsibilities, and broader cybersecurity strategy.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - sales@ibntech.com
Categories
- Artificial Intelligence (AI)
- Technology
- Business
- Education
- Science
- Lifestyle
- Healthcare
- Entertainment
- Politics
- Environment
- Travel
- Finance
- Automobile
- News
- Art
- Causes
- Crafts
- career
- Dance
- Drinks
- Film
- Fitness
- Food
- Games
- Gardening
- Health
- Home
- Literature
- Music
- Networking
- Other
- Party
- Religion
- Shopping
- Sports
- Theater
- Wellness
Read More
Deciding to undergo an aesthetic transformation is an empowering step toward boosting your confidence and refreshing your appearance. It is entirely natural to feel a mix of excitement and apprehension as you prepare for your procedure. Endolift in Riyadh By shifting your focus from the unknown to understanding the process, you can transform that pre-procedure tension into a calm,...

Navigating the competitive landscape of automated interactive systems requires a clear understanding of where the industry is heading over the next decade. Strategic planning heavily relies on accurate foresight, making a detailed Photo Booth/Kiosk Market forecast indispensable for manufacturers and service providers alike. As digital transformation accelerates across various consumer-facing...
Folic Acid Market is expanding as the demand for nutritional wellness solutions and fortified food products continues to rise. The increasing focus on healthy lifestyles has encouraged consumers to pay greater attention to essential vitamins and dietary requirements. Folic acid is recognized as an important nutritional component used across supplements, functional foods, and healthcare...

The increasing prevalence of urinary tract disorders, benign prostatic hyperplasia (BPH), overactive bladder, urinary incontinence, and recurrent urinary tract infections is driving sustained growth in the Urological Medications Market. Urological medications include alpha blockers, anticholinergics, antibiotics, phosphodiesterase inhibitors, and 5-alpha reductase inhibitors that...
تُعتبر مشكلة تساقط الشعر وفقدان كثافته من أكثر التحديات الجمالية والصحية التي تؤرق الرجال والنساء على حدٍ سواء في عصرنا الحالي. ومع التطور المتسارع في مجالات الطب التجميلي والعلاج الخلوي، أصبحت تقنية البلازما الغنية بالصفائح الدموية (PRP) الخيار الطبيعي والآمن الأكثر إقبالاً لتجديد بصيلات الشعر وتنشيط نموها. يتطلع آلاف الأشخاص سنوياً إلى خوض تجربة حقن البلازما للشعر في دبي للوصول إلى نتائج...