
Building Stronger IT Defense With Managed SOC Services India
How Managed SOC Services India Support IT Security
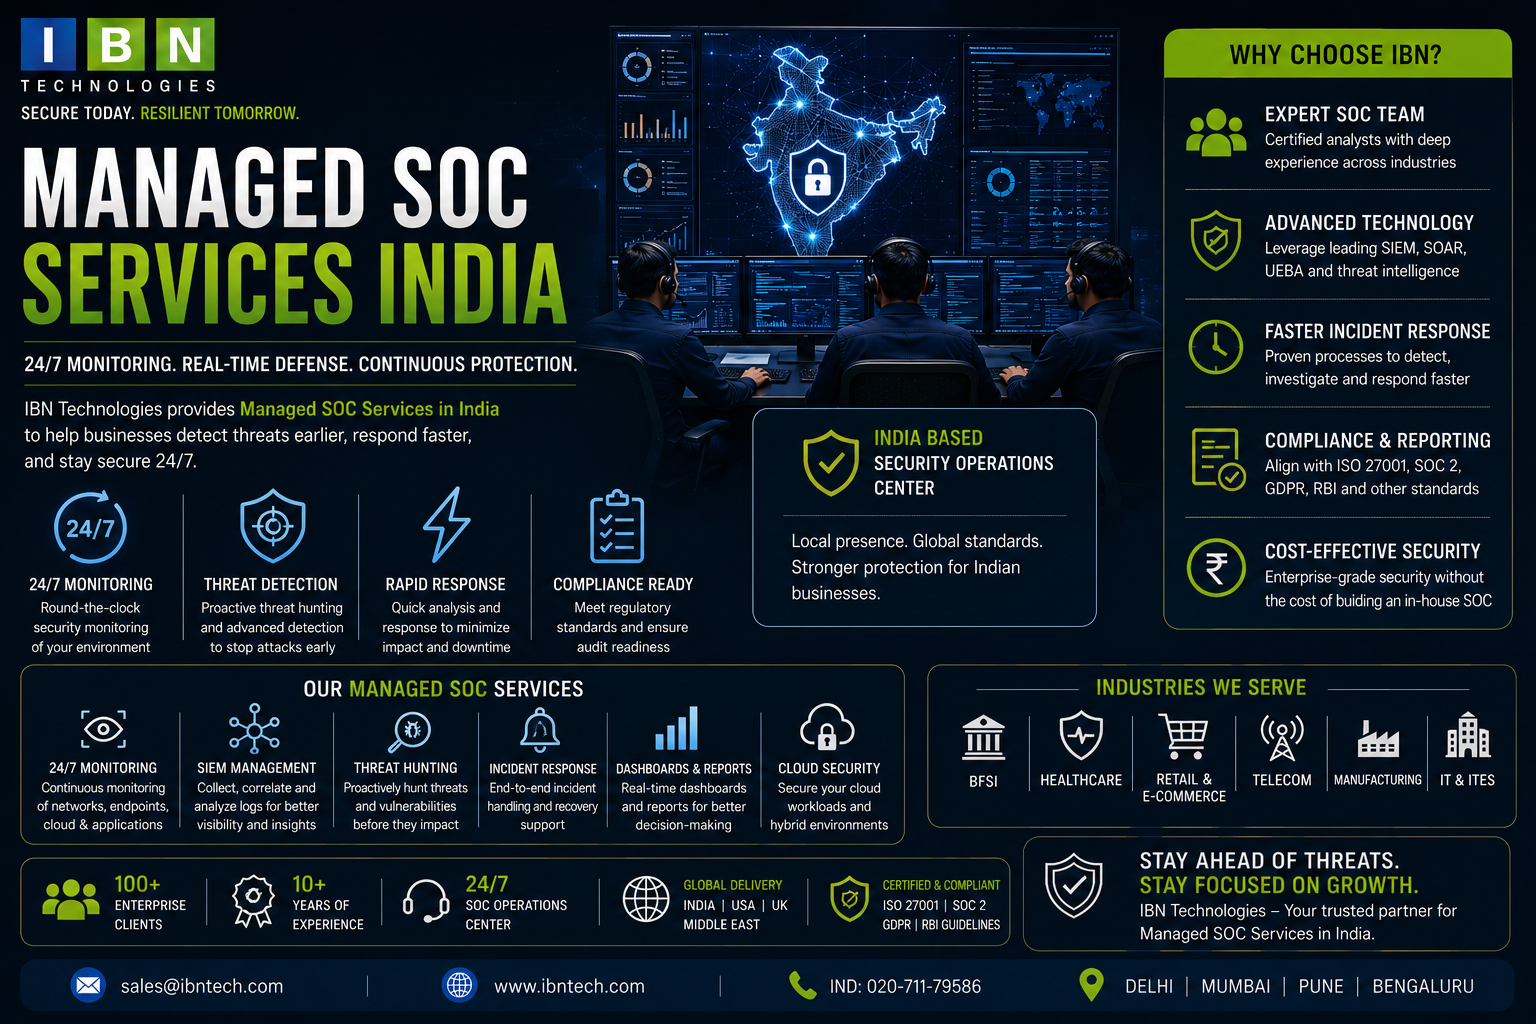
Modern IT environments rarely stay within one office or one data centre. Cloud workloads, remote employees, SaaS applications, endpoints, identity platforms, and business applications create a security environment that needs continuous attention. For many organizations, managed soc services india provide a structured way to monitor security activity and respond to potential threats.
A managed SOC combines security technology with human analysis. It can collect relevant events, correlate activity, investigate suspicious alerts, support incident response, and provide reporting for security and management teams.
Why IT Teams Need Continuous Security Visibility
Security incidents do not follow the working day. An unusual login, suspicious endpoint process, unexpected privilege change, or abnormal network connection can occur while the internal IT team is focused on another priority.
The Visibility Gap: Traditional IT monitoring often focuses on availability and performance rather than detailed security investigation. A system can be operational while still showing signs of unauthorized activity.
The Staffing Challenge: Building an internal SOC requires people with different security skills, defined processes, suitable technologies, and ongoing operational management. Smaller security teams may struggle to maintain continuous coverage while also handling routine IT responsibilities.
The Alert Problem: Security tools can generate large volumes of events. Without appropriate triage and investigation, important signals can become difficult to distinguish from routine activity.
The Response Requirement: Detecting a suspicious event is only part of the process. Teams also need clear escalation procedures and defined responsibilities for containment and recovery.
What Should IT Leaders Consider When Evaluating SOC Costs
Organizations comparing managed soc service provider for IT companies in India cost guide options should look beyond the monthly service fee. The meaningful cost comparison includes technology, staffing, implementation, monitoring coverage, integration, reporting, and the internal effort required to operate the service.
How Does A Managed SOC Service Provider For IT Companies In India Cost Guide Help Planning?
A practical cost assessment should compare the managed model with the resources required to operate equivalent capabilities internally. This includes security analysts, SIEM technology, integrations, infrastructure, maintenance, training, incident response processes, and management overhead.
The purpose is not simply to find the lowest price. It is to understand what security coverage the organization receives for its operational investment.
Technology Requirements: Consider SIEM, endpoint security, network monitoring, cloud visibility, log management, and related security tooling.
People Requirements: Account for analysts, security leadership, incident response expertise, and the need for coverage outside normal office hours.
Operational Effort: Include onboarding, tuning, alert investigation, reporting, rule maintenance, and coordination with internal teams.
Scalability: Consider how costs and operational requirements may change as users, applications, locations, and cloud workloads grow.
How Does Managed SOC Monitoring Work For An IT Environment
A managed SOC generally starts by identifying the systems that matter most to the organization's security posture. Relevant logs and events are then connected to monitoring technologies so analysts can examine activity across the environment.
Data Collection: Security events can come from endpoints, firewalls, applications, servers, identity systems, and cloud environments.
Event Correlation: SIEM technology can connect related events and provide broader context for investigation.
Threat Detection: Detection mechanisms identify suspicious patterns, anomalies, or known indicators of compromise.
Human Analysis: Security analysts review relevant alerts and investigate activity rather than relying entirely on automated notifications.
Incident Escalation: Significant findings move to designated internal stakeholders through agreed procedures.
Response Support: Authorized personnel can then perform containment, remediation, or recovery activities according to the organization's incident response plan.
Can A Managed SOC Service Provider For IT Companies In India Cost Guide Include Cloud Security?
Yes, where the required cloud systems and security events are included within the agreed monitoring scope. IT organizations should identify their cloud platforms, workloads, identities, applications, and administrative activities before defining coverage.
A cloud environment should not be treated as separate from the wider security operation. Authentication, endpoint, network, and application activity may all contribute useful evidence during an investigation.
Which IT Security Events Deserve Priority
Not every event requires the same level of attention. Security teams should prioritize activity according to business impact, asset criticality, user privilege, and potential threat significance.
Privileged Activity: Administrative account changes and unusual privileged access deserve careful monitoring because these accounts can affect important systems.
Identity Anomalies: Unexpected authentication patterns can provide useful signals when investigating compromised credentials.
Endpoint Behavior: Suspicious processes, unauthorized software, or unusual system activity may indicate a security issue.
Network Changes: Unexpected connections or unusual communication patterns can add context to an investigation.
Cloud Activity: Administrative changes, access events, and configuration modifications can be important for organizations operating hybrid environments.
How Can IT Teams Use A Managed SOC Service Provider For IT Companies In India Cost Guide?
IT leaders can use the cost guide concept as part of a broader service evaluation. The review should connect price with measurable scope, operational responsibilities, security coverage, and expected internal effort.
Define Assets: Identify critical infrastructure, applications, endpoints, identities, and cloud workloads.
Define Outcomes: Decide whether the priority is continuous monitoring, improved alert investigation, incident response support, compliance reporting, or broader detection capability.
Define Ownership: Establish which activities remain with internal IT and which fall within the managed service.
Define Escalation: Agree on severity levels, contacts, communication methods, and response responsibilities.
Define Reporting: Determine what security information management and compliance stakeholders need to receive.
What Compliance Considerations Matter For Indian IT Organizations
Indian organizations may need to consider CERT-In requirements and applicable obligations under the Digital Personal Data Protection framework, depending on their activities and circumstances. Organizations using ISO 27001 may also integrate security monitoring and incident management into their broader information security management system.
Compliance should not be treated as a substitute for security operations. Monitoring, access controls, incident response, risk management, and documentation should work together as part of a wider governance structure.
Is Managed SOC Monitoring Suitable For Growing IT Teams?
It can be useful when an organization needs broader security coverage without immediately creating every internal SOC capability. The operating model can also support internal security personnel by taking on defined monitoring and investigation responsibilities.
The arrangement works best when responsibilities are documented clearly and internal teams retain appropriate control over business decisions and authorized response actions.
FAQs
What Does A Managed SOC Do For An IT Company?
A managed SOC monitors security events, investigates suspicious activity, supports threat detection, and escalates significant findings. The exact responsibilities depend on the agreed service scope.
Does SIEM Replace A SOC?
No. SIEM provides technology for collecting, correlating, and analyzing security events, while a SOC includes the people, processes, investigation, escalation, and response functions needed to operate security monitoring.
Should IT Companies Outsource Their Entire Security Operation?
Not necessarily. Some organizations use fully managed services, while others use co-managed arrangements that divide responsibilities between internal personnel and external security specialists.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - sales@ibntech.com