Managed SOC Service Provider: Critical Security Support for Indian IT
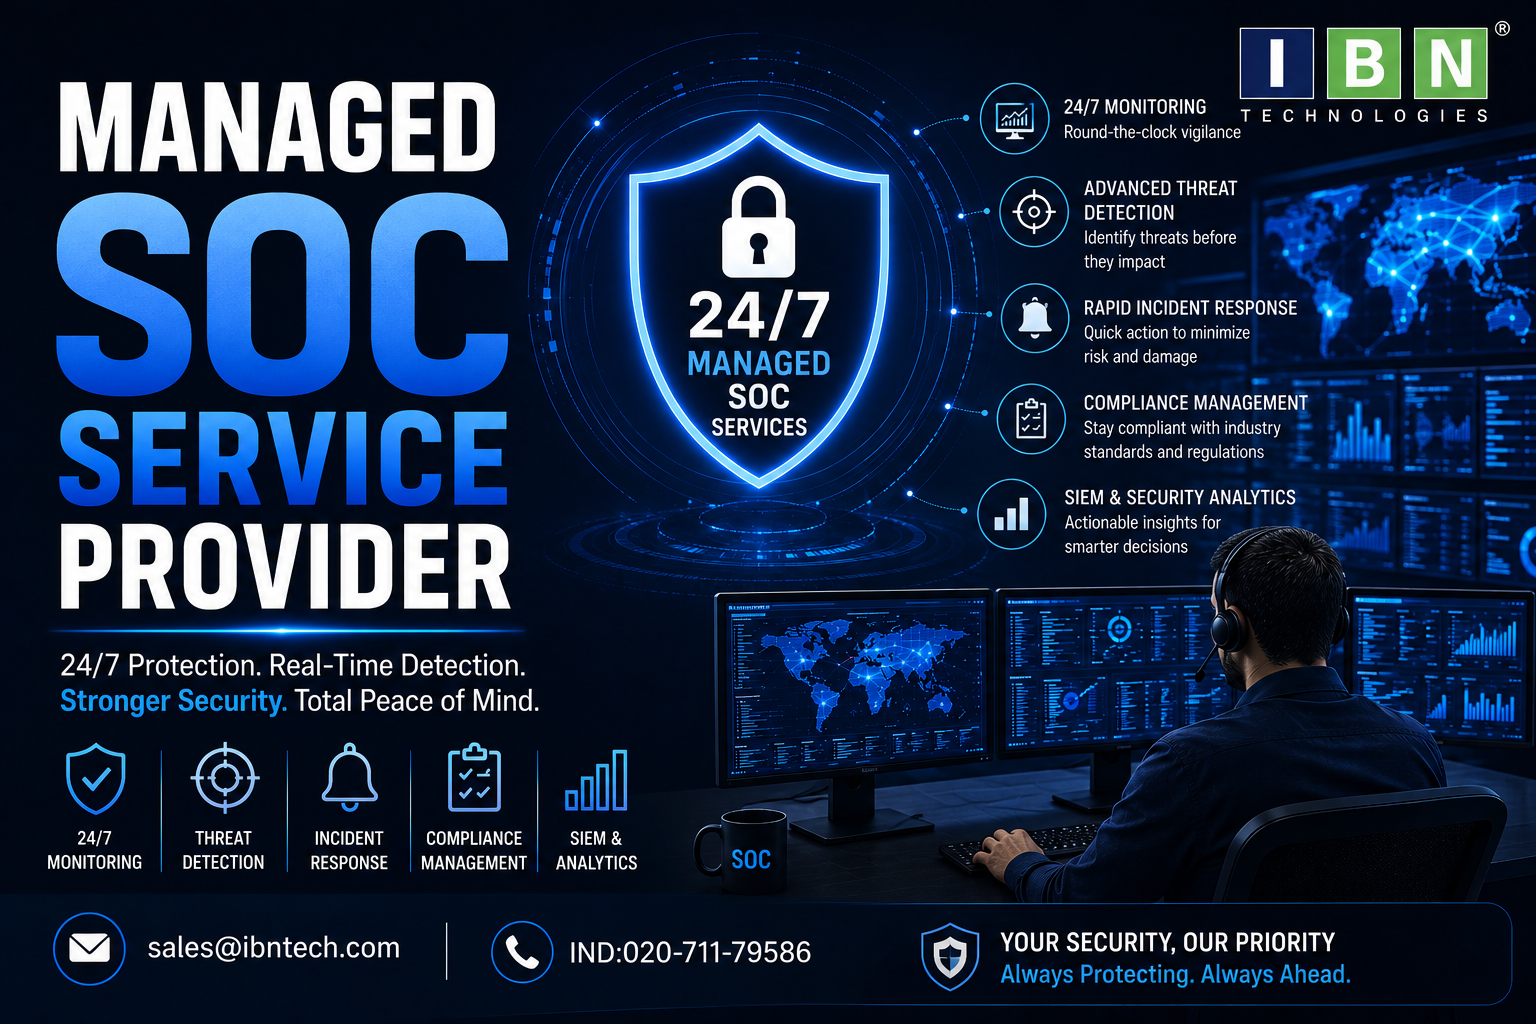
How a Managed SOC Service Provider Strengthens Security for Indian IT Businesses
Indian IT businesses operate across applications, cloud environments, endpoints, networks, remote users, and business systems. As these environments expand, security teams have to deal with more security events while continuing to support everyday technology operations.
This is where a managed soc service provider can become part of an organisation's security operations model. Instead of depending entirely on internal teams to monitor and investigate security events, businesses can use managed SOC capabilities for continuous monitoring, alert analysis, threat detection, and incident escalation.
The real value is not simply having another cybersecurity service. It is creating a more structured way to understand what is happening across the IT environment and determine which events require attention.
Why a Managed SOC Service Provider Matters for Indian IT Businesses
A managed SOC is a security operations capability that monitors relevant security events, analyses alerts, investigates suspicious activity, and supports defined escalation and response processes.
For Indian IT businesses, this can provide an organised approach to security monitoring when technology environments become too complex for occasional manual review.
Security visibility is particularly important when employees, applications, cloud resources, endpoints, and network infrastructure are continuously generating activity.
Why Traditional IT Monitoring Can Leave Security Gaps
IT Monitoring and Security Monitoring Are Not the Same
Traditional IT monitoring generally focuses on availability, performance, infrastructure health, and operational issues. Security monitoring has a different objective: identifying activity that may indicate unauthorised access, malicious behaviour, or another security concern.
An organisation can have systems running normally while suspicious activity is taking place within those systems.
This distinction is one reason businesses evaluate soc companies when they need dedicated security operations support. A SOC focuses on security events and provides processes for reviewing, investigating, and escalating potentially important activity.
For an IT organisation, this additional security perspective can complement existing infrastructure and technology operations.
How a Managed SOC Service Provider Works
A managed SOC generally operates through a combination of technology, security analysts, defined processes, and communication procedures.
Security Event Collection
Relevant security events are collected from agreed technology environments. These may include systems, applications, endpoints, network infrastructure, or other monitored sources.
Alert Analysis
Security events are assessed to determine whether they require further investigation. This helps separate routine activity from events that may represent a genuine security concern.
Threat Detection
Security analysis can identify suspicious patterns and activity that may require attention from the organisation's security or IT teams.
Investigation
When an alert requires deeper examination, analysts can review available security information to understand the context and potential significance of the event.
Escalation
If an event meets predefined criteria, findings can be communicated to the appropriate internal stakeholders for further action.
This workflow helps transform large volumes of security information into a more manageable operational process.
What Indian IT Businesses Gain From Managed SOC Operations
A managed SOC can support IT organisations in several practical ways.
First, it can improve security visibility. Instead of security events remaining distributed across different systems, monitoring can provide a more organised view of relevant activity.
Second, it can reduce the investigation burden. Internal IT teams may have competing responsibilities, making it difficult to examine every security notification in depth.
Third, it can establish clearer escalation processes. When potentially serious activity is identified, predefined communication and response procedures can reduce uncertainty.
Fourth, it can support continuous security operations. Security monitoring becomes an ongoing process rather than something performed only after a suspected incident.
The exact benefits depend on the organisation's environment, monitoring scope, and internal security processes.
A Practical IT Use Case
Consider an Indian software company with employees working across multiple locations and accessing cloud applications and internal systems.
An employee account suddenly produces an unusual authentication event.
The event alone does not necessarily confirm an attack. However, a security operations team can examine related activity and determine whether additional investigation is warranted.
A managed SOC can review the available security information, investigate relevant alerts, and escalate the event when it meets the organisation's defined criteria.
This creates a structured path from detection to investigation rather than leaving the internal IT team to manually interpret every notification.
How to Evaluate a Managed SOC Service
IT leaders should evaluate a managed SOC based on operational fit rather than simply counting features.
Key areas include:
- Which systems and environments will be monitored?
- How are security alerts prioritised?
- What investigation process is followed?
- What information is shared when an incident is escalated?
- Which actions remain the responsibility of the internal IT team?
- What security reporting is provided?
- How is monitoring adjusted when the technology environment changes?
- How are recurring security events reviewed?
These questions help organisations understand how the service will work in real operating conditions.
Building Better Security Operations With Internal IT Teams
A managed SOC should complement—not replace—the organisation's internal technology and security responsibilities.
Internal teams still need ownership of business priorities, access decisions, security policies, infrastructure changes, and response actions.
The managed SOC can provide additional monitoring and analysis capacity within this structure.
Clear responsibilities are therefore important. Organisations should establish who receives escalations, who approves response actions, and how significant incidents are communicated.
Best Practices for Indian IT Teams
IT organisations considering managed SOC operations can establish a stronger foundation by:
- Identifying critical systems that require security monitoring
- Defining security escalation criteria
- Documenting internal response responsibilities
- Reviewing monitoring coverage whenever infrastructure changes
- Establishing clear communication channels for significant events
- Reviewing recurring alerts and investigation patterns
- Regularly assessing whether monitored environments still match business requirements
These practices help connect security monitoring with everyday IT operations.
Managed SOC and Security Governance in India
Managed SOC operations can contribute to a broader cybersecurity framework by supporting security monitoring, threat detection, investigation, and incident response processes.
However, SOC monitoring is not a substitute for the organisation's complete cybersecurity program.
IT businesses should continue to maintain appropriate security policies, access controls, vulnerability management, employee awareness, backup practices, and other relevant security measures.
A managed SOC works most effectively when it is integrated into this wider security structure.
Creating a More Responsive IT Security Model
As Indian IT environments become increasingly connected, security monitoring needs to keep pace with changing infrastructure and user activity.
A managed soc service provider can help organisations establish a structured model for monitoring, alert analysis, threat detection, investigation, and escalation.
For Indian IT businesses, the goal should not be to collect more security alerts. It should be to create useful visibility and a repeatable security operations process that helps internal teams recognise and respond to potentially significant activity.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - sales@ibntech.com
Categories
- Artificial Intelligence (AI)
- Technology
- Business
- Education
- Science
- Lifestyle
- Healthcare
- Entertainment
- Politics
- Environment
- Travel
- Finance
- Automobile
- News
- Art
- Causes
- Crafts
- career
- Dance
- Drinks
- Film
- Fitness
- Food
- Games
- Gardening
- Health
- Home
- Literature
- Music
- Networking
- Other
- Party
- Religion
- Shopping
- Sports
- Theater
- Wellness
Read More
The POCT Molecular Diagnostics Market is experiencing significant growth as healthcare systems worldwide increasingly adopt rapid, accurate, and decentralized diagnostic solutions. Point-of-care testing (POCT) molecular diagnostics enables healthcare professionals to detect diseases quickly near the patient location, reducing dependency on centralized laboratories and improving clinical...
Slow Release Nitrogen Fertilizer Market Report Overview The Slow Release Nitrogen Fertilizer Market report provides a comprehensive and analytically structured examination of the Slow Release Nitrogen Fertilizer market. Based on rigorous primary and secondary research methodologies, it evaluates competitive dynamics, technological advancements, regulatory environments, and evolving...
Wearable healthcare devices are smart electronic technologies worn on the body that continuously monitor, record, and analyze health-related information in real time. These devices enable individuals and healthcare professionals to track critical health metrics such as heart rate, blood pressure, blood glucose levels, oxygen saturation, sleep quality, physical activity, and other vital...
The North America Food Fortifying Agents Market is witnessing significant growth as the demand for nutritionally enhanced food products continues to increase across the world. According to the latest market study by The Insight Partners, the global Food Fortifying Agents Market is projected to expand at a CAGR of 10.5% during the forecast period from 2026 to...

Beverage equipment repair services are specialized services that restore the functionality and performance of beverage processing machinery, minimizing downtime and ensuring production continuity. The Beverage Equipment Repair Services market is projected to grow substantially, driven by stringent food safety standards and the need for reliable equipment. These services are essential...