


Aviation Cyber Security Market Outlook Amid Rising Digital Threats
The aviation industry is entering an increasingly connected digital era in which technology plays an important role in almost every stage of air transportation. From booking and passenger processing to aircraft operations and airport infrastructure, digital systems have become central to aviation activities. This connectivity creates opportunities for improved coordination and efficiency while also introducing cybersecurity challenges. As aviation organizations expand their digital infrastructure, cybersecurity is becoming an increasingly important element of operational planning.
The growing focus on aviation threat intelligence highlights the industry's transition toward proactive cybersecurity. Threat intelligence can help organizations understand emerging attack methods, suspicious activities, vulnerabilities, and potential sources of risk. When incorporated into security operations, such intelligence can support better monitoring, investigation, preparedness, and response.
One of the primary cybersecurity concerns in aviation is the protection of interconnected systems. Airlines and airports use numerous platforms that exchange information across internal and external networks. Aircraft may also interact with ground-based systems and communication infrastructure. This interconnected environment requires security teams to maintain visibility across multiple technology layers.
Ransomware, malware, phishing, credential compromise, and unauthorized access represent different categories of cybersecurity risks that aviation organizations may need to consider. Each threat can affect systems in different ways and therefore requires appropriate preventive and responsive controls. Security teams may use a combination of endpoint protection, network monitoring, authentication, encryption, access controls, and incident response capabilities.
Phishing and social engineering are particularly relevant because they target users rather than only technical vulnerabilities. Employees may receive fraudulent messages designed to obtain credentials or encourage unsafe actions. Aviation organizations can reduce exposure by combining email security technologies with employee awareness training and clear procedures for reporting suspicious communications.
Identity and access management provides another layer of protection. Aviation systems may be accessed by employees, contractors, partners, service providers, and administrators. Managing these identities requires appropriate authentication mechanisms and permissions. Organizations can apply role-based access, multi-factor authentication, privileged access controls, and periodic access reviews to strengthen security.
Airport cybersecurity presents its own set of challenges. Airports combine operational systems with passenger-facing technologies, physical security infrastructure, communication systems, and commercial services. Many of these systems may be operated by different stakeholders. Coordinating security responsibilities across such an environment requires defined policies, communication channels, and incident response procedures.
Airlines must also protect sensitive passenger and business information. Data can include booking details, identification information, payment-related information, employee records, and operational information. Data security practices such as encryption, access management, monitoring, and secure data handling can help protect these environments.
Cloud technologies are increasingly becoming part of aviation infrastructure. Cloud platforms can provide scalable resources and support distributed operations, but they also require careful security management. Misconfigured cloud resources, weak credentials, inadequate access controls, and insufficient monitoring can create vulnerabilities. Organizations therefore need cloud security practices integrated into their broader cybersecurity strategies.
Artificial intelligence and machine learning can support threat detection and security analytics. These technologies can examine patterns across large volumes of information and potentially identify anomalies more quickly. They can assist security teams by prioritizing alerts and supporting automated analysis. Nevertheless, human oversight remains essential when interpreting security events and determining appropriate responses.
Cybersecurity resilience also requires preparedness for incidents. Organizations should establish procedures for detection, containment, investigation, recovery, and communication. Testing these procedures through exercises can help identify gaps and improve coordination among technical and operational teams.
Another consideration is cybersecurity throughout the aviation supply chain. Aviation organizations depend on numerous technology providers, software platforms, equipment manufacturers, maintenance organizations, and service providers. Security weaknesses within one part of the supply chain can create risks elsewhere. Supplier assessments, contractual security requirements, access controls, and continuous monitoring can contribute to stronger supply-chain security.
Overall, the Aviation Cyber Security Market is developing alongside the continued digital transformation of aviation. The focus is shifting toward integrated security frameworks that combine technology, employee awareness, governance, monitoring, threat intelligence, and incident response. As aviation infrastructure becomes more interconnected, maintaining cybersecurity resilience will remain an important part of protecting digital aviation operations.
FAQs
FAQ 1: What is aviation threat intelligence?
Aviation threat intelligence involves collecting and analyzing information about cybersecurity threats, vulnerabilities, attack techniques, and suspicious activities relevant to aviation environments.
FAQ 2: How can aviation organizations improve cybersecurity resilience?
Organizations can strengthen resilience through continuous monitoring, employee training, access management, vulnerability assessments, threat intelligence, incident response planning, security testing, and coordinated communication procedures.
Categories
- Artificial Intelligence (AI)
- Technology
- Business
- Education
- Science
- Lifestyle
- Healthcare
- Entertainment
- Politics
- Environment
- Travel
- Finance
- Automobile
- News
- Art
- Causes
- Crafts
- career
- Dance
- Drinks
- Film
- Fitness
- Food
- Games
- Gardening
- Health
- Home
- Literature
- Music
- Networking
- Other
- Party
- Religion
- Shopping
- Sports
- Theater
- Wellness
Read More
The Spectrum Analyzer Market Share distribution reveals a competitive landscape where established test and measurement giants vie for dominance in a rapidly evolving sector. The market is moderately consolidated, with the top four players projected to exceed 50% market share by 2025 . Key players such as Keysight Technologies, Tektronix, Rohde & Schwarz, Anritsu, and National...
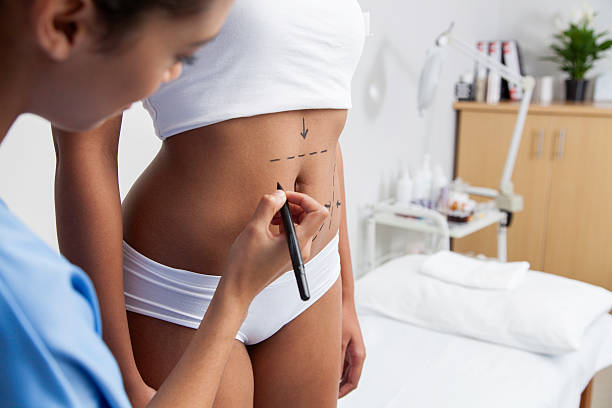
Achieving a well-defined body shape can sometimes be challenging, even with regular exercise and a balanced diet. Certain areas of stubborn fat may remain resistant to healthy lifestyle efforts, making it difficult to achieve your desired physique. Many people choose Liposuction procedure in Riyadh (كم سعر عملية شفط الدهون في السعودية) as an effective body contouring solution to target...
The technological architecture behind diagnostic image transfer has shifted dramatically from localized hardware to cloud-native, scalable solutions. Organizations transitioning away from legacy infrastructure consult a Medical Image Exchange System Market assessment to understand how software-as-a-service (SaaS) and hybrid frameworks optimize operational workflows. Cloud-based deployment...

Automotive LiDAR Market is evolving with increasing deployment of solid-state LiDAR technologies that offer improved durability and cost efficiency. These innovations are making LiDAR solutions more suitable for mass-market automotive applications. The automotive LiDAR market accounted for US$ 415.1 million in 2018 and is expected to grow at a CAGR of 30.4% during the forecast...
Institutional Frameworks, Inpatient Units, and Home-Based Care Solutions Palliative care delivery across GCC countries utilizes a hybrid architecture of inpatient units, outpatient clinics, and community-based home healthcare services. To optimize resource allocation, healthcare authorities are building specialized step-down facilities and community outreach networks to deliver continuous...
